Let us show you everything Luma can do.

Our commitment to trust

Luma's security, privacy, and compliance programs help put patients at the center of everything they do.

With AI rapidly transforming how healthcare is delivered, our longstanding commitment to information security holds more importance than ever. Our customers trust Luma’s AI with key operational processes. We’re dedicated to rigorous excellence in security, and continue to validate that with the best security frameworks available.”

Denis Savenko

Head of Information Security and Compliance
Compliance and certifications

Our security program is built on internationally recognized information security and privacy frameworks. We undergo independent third-party audits annually and maintain a dedicated in-house security and compliance team to ensure ongoing protection and regulatory alignment.

HIPAA-compliant

Zero-retention AI

ISO 27001:2022

HITRUST CSF r2

HITRUST ai2

SOC 2 Type II

US-EU Privacy Framework

GDPR

TX-RAMP Level 2

Contact Luma's security team for questions about Luma's security program.

Contact our security team

If you have questions about our security program, privacy practices, or believe you have identified a potential security vulnerability, our dedicated security and compliance team is available to help. We encourage responsible disclosure and take all reports seriously.
luma-monitor-platform-status

Monitor platform status

Access real-time information about system availability, historical uptime performance, maintenance events, and incident communications. Subscribe to alerts to receive proactive notifications about service interruptions or planned maintenance activities.

All system access at Luma Health follows the principles of Zero Trust and Least Privilege and is centrally managed, with Single Sign On (SSO) required wherever possible. Context-aware controls ensure that certain conditions are met, such as device type encryption and location, before logins are granted.

We enforce Multi-Factor Authentication across the organization. All access is role-based, and requires management and/or system owner approval. Luma Health’s internal audit team performs access entitlement reviews every 60 days for all accounts.
We operate a modern microservices-based infrastructure that is architected for high-availability with zero single points of failure. All of our infrastructure is managed via code and dynamically scales up and down based on system load and demand.
We have a fully-documented SDLC which follows the OWASP Top Ten. All development is performed in-house, and all new code as well as changes to existing code are subject to Static and Dynamic Application Security Testing (SAST and DAST) and peer review before being considered for a production release.

Every change and release follows our change control process, which includes peer review, testing and validation in lower environments, a backout plan, management approval, and separation of duties between development and release activities.
We perform automated vulnerability scans of our infrastructure monthly, as well as continuous monitoring and scanning of any emerging threats. New infrastructure targets are automatically added to the scan rotation. We partner with a third party to perform external penetration testing annually. Any discovered vulnerabilities are remediated in line with our defined schedule.
All employees are provided with a Luma Health-owned and controlled device that is centrally managed via an MDM solution. All devices are protected by centrally-managed security controls such as Endpoint Detection and Response (EDR), next Generation Anti-Virus, firewalls, device encryption, activity lock, and data loss prevention.
All employees are subject to a background check before joining Luma Health, and are required to complete information security Training, HIPAA training, and policy attestation as part of the onboarding process. Information security training is performed on an ongoing basis, which includes simulated phishing tests.
We have infrastructure deployed in multiple AWS Availability Zones with real-time replication to meet a 99.9% uptime target. Our code-based microservices architecture allows us to quickly deploy a production instance into any AWS data center should the need arise. We fully test our Business Continuity and Disaster Recovery function annually.
Luma Health’s AI-enabled products are built to be ISO 42001 compliant. These products operate under a zero-retention model and do not store data long-term. Customer and patient data is not shared with or made available to other customers and is not shared with or made available to any of our partners or service providers. Customer data is not used to train, retrain, or improve any models.

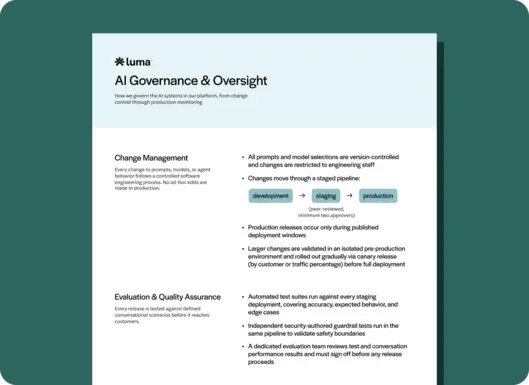
See for more detail on Luma's AI, trust, and governance.
We use your data only to provide contracted services. We never share or sell your data to any third parties, and your data is never used for advertising purposes.

We comply with the EU-U.S. Data Privacy Framework (EU-U.S. DPF), the UK Extension to the EU-U.S. DPF, and the Swiss-U.S. Data Privacy Framework (Swiss-U.S. DPF) as set forth by the U.S. Department of Commerce. To learn more about the Data Privacy Framework (DPF) program, and to view our certification, please visit https://www.dataprivacyframework.gov.

Let's talk

We’d love to discuss how Luma’s end-to-end AI automation can get patients to care faster and increase revenue. Get in touch to book your personalized walkthrough.